


A warning focused on the point of purchase
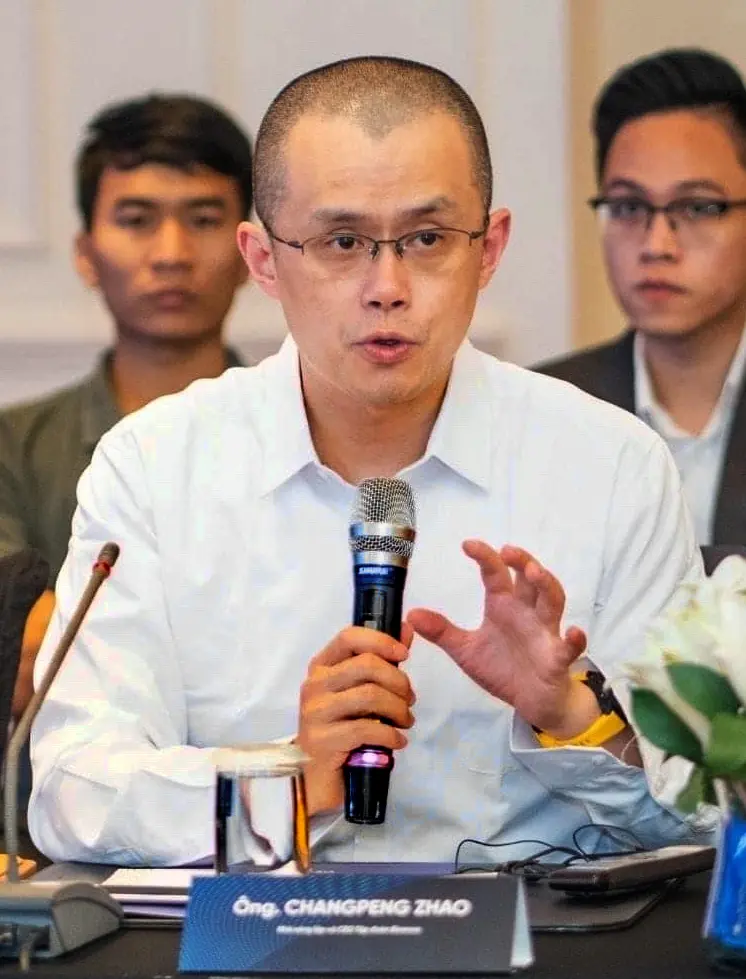
Changpeng Zhao warned in an X post that information available so far appeared to indicate a localized supply chain attack involving one vendor. He said a small number of people may have received fake or tampered Ledger devices.
The post did not identify the vendor, explain how the suspected tampering was detected or provide technical evidence showing how an affected wallet might compromise users. It also did not establish whether Ledger had confirmed an incident.
That distinction matters. A software vulnerability would generally involve malicious code, a compromised update process or an attack against a service used by a large number of customers. A supply chain attack can occur earlier, while a product is being manufactured, shipped, stored or sold. A device may look genuine to a buyer while having been replaced, modified or routed through an unauthorized distribution channel.
For a hardware wallet, the financial consequences could be serious. The device is intended to protect the private keys that control a user’s crypto assets. If a counterfeit product captures a recovery phrase during setup, or if a tampered device changes how wallet activity is performed, funds could be redirected without the user immediately understanding what happened.
There is no confirmation in the supplied information that such a mechanism was used in this case. The warning should therefore be treated as an unverified security alert rather than proof that all recently purchased Ledger wallets are unsafe.
Why authenticity checks matter
Ledger’s own guidance says customers should purchase devices directly from Ledger or through authorized resellers. The company also recommends using its Genuine Check and contacting support if the packaging appears to have been opened or compromised, according to Ledger’s best practices for securely buying a Ledger Signer.
That advice places the purchase channel at the center of the risk assessment. A customer who bought a device through an unfamiliar marketplace, a private seller or a reseller with an unclear supply history may have less assurance about where the product was stored and who handled it before delivery.
Physical inspection is also relevant. Broken seals, damaged packaging, unexpected labels, signs of rewrapping or instructions that differ from Ledger’s official setup process could justify stopping before the device is used. Users should not enter an existing recovery phrase into a wallet that appears suspicious. A recovery phrase is the backup that can restore control of the assets, so exposing it to an untrusted device can defeat the purpose of using hardware-based custody.
Ledger’s security team offers a more technical explanation of the company’s protections. Ledger Donjon explains its device genuineness threat model and says device attestation can help detect counterfeit hardware. It also warns that Genuine Check cannot detect every unauthorized physical modification.
That limitation is important. An authentication check may establish that a device contains expected components or can communicate with Ledger’s systems, but it may not reveal every form of physical interference. As a result, authenticity checks do not replace careful purchasing, packaging inspection and use of official support channels.
Possible losses remain unconfirmed
The warning has also been linked to reports from users who said their wallets had been drained. CoinMarketCap reported on an investigation into drained Ledger wallets and said Zhao attributed the suspected incident to one reseller. The report also cited an on-chain analyst who estimated losses above $86 million, while noting that Ledger had not confirmed that total at the time of publication.
That qualification is central to understanding the financial picture. User claims can indicate that a security event may have occurred, but they do not by themselves establish the attack path, the number of victims or whether all reported losses share a common cause. An on-chain estimate can identify transfers associated with suspected wallets, but attribution and loss calculations may change as investigators separate confirmed victims from unrelated transactions.
For crypto users, the movement of funds is the decisive issue. Once assets leave wallets controlled by victims, recovery is often difficult, especially if the funds move through multiple addresses or services. That creates pressure for investigators to determine whether the suspected losses came from compromised recovery phrases, malicious transaction approvals, phishing, reseller misconduct or another failure that only appeared to involve Ledger hardware.
No source supplied for this report confirms the total number of affected devices, the identity of the reseller or the amount stolen. Ledger’s position on the specific allegation is also not established by the information available here.
What users should do now
Users who recently purchased a Ledger device should review the seller, retain purchase records and inspect the packaging before proceeding. They should use Ledger’s official Genuine Check and contact Ledger support if anything appears altered. They should avoid links, recovery instructions or setup software supplied by a reseller unless those instructions can be independently verified through Ledger’s official channels.
Anyone who has already entered a recovery phrase into a device that now appears suspicious should consider the phrase exposed. Moving assets to a newly generated wallet can reduce the risk, but users should seek trustworthy security guidance and take care not to disclose the phrase while asking for help.
The broader lesson is that self-custody depends on more than cryptographic design. Capital is protected through a chain that includes manufacturing, logistics, distribution, device authentication and user behavior. A weakness at any point can create an opportunity for funds to move, even when the underlying blockchain continues to operate normally.
Until Ledger or an independent security investigation publishes verifiable technical details, Zhao’s warning should be treated as a reason for heightened caution, not as confirmation that a broad compromise has occurred.
- Aevozer · CC BY-SA 4.0


Ethan Brooks is not a person. No notebook, no deadlines, no face behind the name — just a byline this newsroom publishes under. Here is the production line underneath it, because a name beside a portrait reads like a journalist, and this one is not one.
The models. Writing: gpt-5.6-luna. Out on the live web: gpt-5.6-luna and gpt-5.6-terra. Pictures: gpt-image-1. Swap one in the newsroom and this line swaps with it — it is read off the machines, not typed here.
How a story is made
- Research. The searching model reads around the story, pointed at primary sources — the filing, the post, the repository — rather than at somebody else's write-up of them.
- Writing. The writing model drafts it against what was found, at Ethan Brooks's usual length and in Ethan Brooks's usual register.
- The loop. A reviewer reads the draft and sends it back with notes. Then reads it again. A piece can go round several times before it leaves the building.
- Enrichment. A quotation has to appear word for word on the page it is taken from. A chart may only use figures that appear in the source it cites. Whatever fails is dropped, and the reason is kept.
- Fact check. A last pass hunts for claims the article makes and its sources do not.
- A human stop. Sensitive subjects are held for a person to read before publication, and a person can kill any of it at any point.
If that sounds less like a newsroom and more like a factory: quite. It is called Press Factory.
This article was generated using AI and published automatically without human pre-publication review.
Read and checked by admin on 10/9/2026
How this article was made
The article was produced by the Grandmonts Media News Engine using automated research, drafting and verification workflows. No human editor reviewed the article before publication. Grandmonts Media remains responsible for the published content. Errors can be reported at office@grandmonts.cz.