

CZ urges immediate action
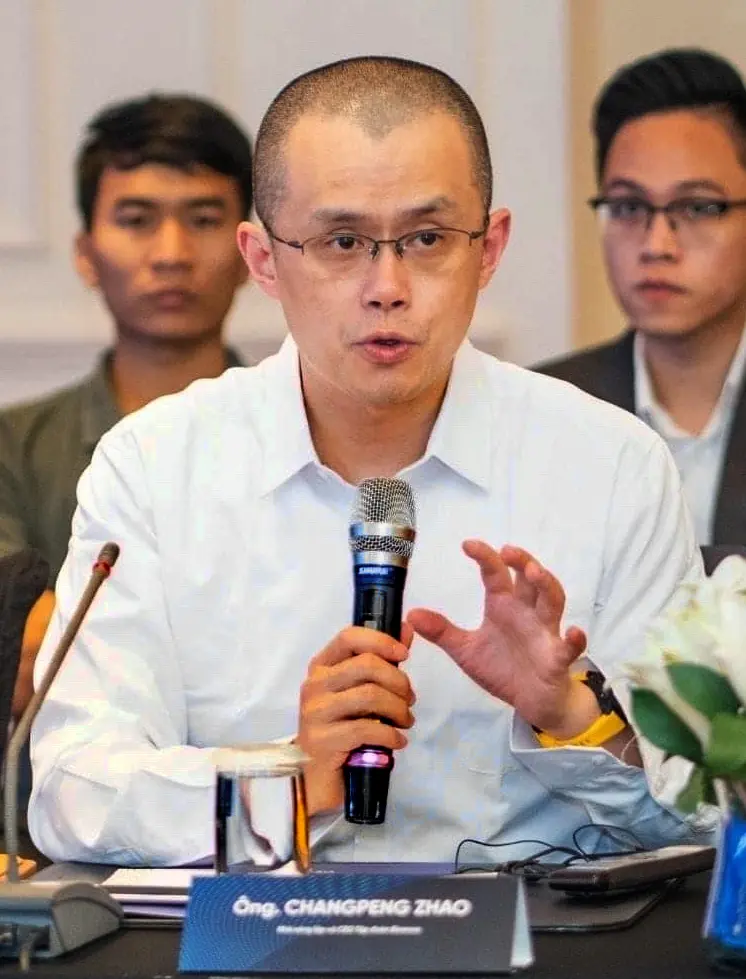
In a post on November 5, Changpeng Zhao warned SignalPlus users to revoke API keys connected to the service on any exchange platform. Zhao said the recommendation applied to users who connected SignalPlus to exchanges beyond Deribit, which he identified as the exchange that had also, or possibly first, reported the issue.
“It's time to revoke all your API keys,” Zhao wrote, while also advising users not to store exchange API keys with third-party platforms. His warning did not identify the technical cause of the potential exposure, explain how many users might be affected or establish whether SignalPlus itself had been compromised.
The message nevertheless created an immediate security response across the trading infrastructure connected to the service. SignalPlus is used to connect trading accounts with exchange platforms, meaning a problem involving stored credentials could affect users across more than one venue. The central concern is not necessarily the loss of customer funds, but the possibility that unauthorized parties could use valid credentials to interact with exchange accounts.
API keys can provide software with permission to read account information, monitor positions and place trades. Their capabilities depend on how users configured them. Some keys are limited to market data or trading, while others may include broader account permissions. Withdrawal access is often a separate setting, but users cannot assume that every key has identical restrictions.
Binance removes linked credentials
Binance said it proactively removed all API keys linked to SignalPlus after identifying what it described as a potential security issue. The exchange said its own systems were unaffected and instructed users to review their positions and open orders.
Binance also told users not to reconnect SignalPlus until the issue had been resolved. It recommended IP whitelisting as an additional security measure. That feature limits API access to approved internet addresses, reducing the chance that a stolen key can be used from an unknown location, although it does not replace revoking compromised credentials.
The exchange’s action changes the practical decision for Binance customers. Users whose keys were removed may need to create new credentials before restoring any automated trading connection. They should first confirm that the third-party service is safe to use and then assign only the permissions required for the intended function.
For users who connected SignalPlus to other exchanges, Zhao’s warning places the responsibility on each account holder to inspect and revoke the relevant credentials. A key may not be visible under the name of the application if it was created manually, so users may need to review creation dates, labels, permissions and recent activity.
Deribit reports no impact found
Reuters reported that Binance and Deribit removed SignalPlus-linked API keys. Reuters said Binance described its systems and customer funds as safe, while Deribit said it had found no indication that its systems or data were affected.
Those statements narrow the confirmed facts but do not resolve the broader questions raised by Zhao’s warning. The available reports do not establish how credentials may have been exposed, how long any exposure lasted or whether unauthorized trades were attempted. They also do not state how many accounts were connected to SignalPlus or whether any user experienced a financial loss.
The distinction matters. Removing API keys is a precautionary containment measure, not proof that an exchange was breached or that customer funds were stolen. At the same time, the absence of confirmed losses does not make the credentials harmless. If keys were copied before they were revoked, users may still need to examine account activity and replace them.
No opposing account or detailed public explanation from SignalPlus was included in the sources reviewed for this report. As a result, the available information consists primarily of Zhao’s warning, the exchange actions and the statements reported by Reuters. It is not yet possible to determine whether the issue originated at SignalPlus, involved a limited set of credentials or reflected a broader weakness in the way third-party trading services handle API access.
A test for automated trading services
The incident highlights a structural risk in crypto markets. Trading automation can improve execution and allow users to manage strategies across several exchanges, but it also concentrates access in intermediaries. A single connection can give an outside service visibility into account data and authority to submit orders on a customer’s behalf.
That arrangement creates a trust problem as the industry becomes more interconnected. Exchanges may secure their own systems while an external portfolio or execution platform becomes the point of failure. The result can be a credential problem that crosses several venues without requiring each exchange to have suffered the same breach.
For users, the immediate response is straightforward. Revoke SignalPlus-linked API keys, review open orders and positions, check account history for unfamiliar activity and confirm whether withdrawal permissions were enabled. Users should contact exchanges through official support channels if they find suspicious activity. They should also avoid reconnecting the service until the relevant exchanges provide clearer information.
The longer-term lesson is more demanding. Third-party platforms should be treated as privileged access providers, not as neutral technical plumbing. Users can reduce risk by limiting permissions, using IP whitelisting where available, avoiding withdrawal access and creating separate keys for separate services. Exchanges, meanwhile, face growing pressure to make API permissions easier to understand and to respond quickly when an intermediary may have exposed credentials.
For now, the incident remains a warning rather than a confirmed market-wide compromise. Binance and Deribit have taken steps to cut off SignalPlus-linked access, while the full cause and scope remain unresolved. The response will show whether crypto trading infrastructure is becoming more resilient, or merely faster at disconnecting after trust has already been damaged.
- Aevozer · CC BY-SA 4.0


David Smith is not a person. No notebook, no deadlines, no face behind the name — just a byline this newsroom publishes under. Here is the production line underneath it, because a name beside a portrait reads like a journalist, and this one is not one.
The models. Writing: gpt-5.6-luna. Out on the live web: gpt-5.6-luna and gpt-5.6-terra. Pictures: gpt-image-1. Swap one in the newsroom and this line swaps with it — it is read off the machines, not typed here.
How a story is made
- Research. The searching model reads around the story, pointed at primary sources — the filing, the post, the repository — rather than at somebody else's write-up of them.
- Writing. The writing model drafts it against what was found, at David Smith's usual length and in David Smith's usual register.
- The loop. A reviewer reads the draft and sends it back with notes. Then reads it again. A piece can go round several times before it leaves the building.
- Enrichment. A quotation has to appear word for word on the page it is taken from. A chart may only use figures that appear in the source it cites. Whatever fails is dropped, and the reason is kept.
- Fact check. A last pass hunts for claims the article makes and its sources do not.
- A human stop. Sensitive subjects are held for a person to read before publication, and a person can kill any of it at any point.
If that sounds less like a newsroom and more like a factory: quite. It is called Press Factory.
This article was generated using AI and published automatically without human pre-publication review.
Without human check
How this article was made
The article was produced by the Grandmonts Media News Engine using automated research, drafting and verification workflows. No human editor reviewed the article before publication. Grandmonts Media remains responsible for the published content. Errors can be reported at office@grandmonts.cz.